
SIEM Monitored 24x7 by a SOC for ICT Operations
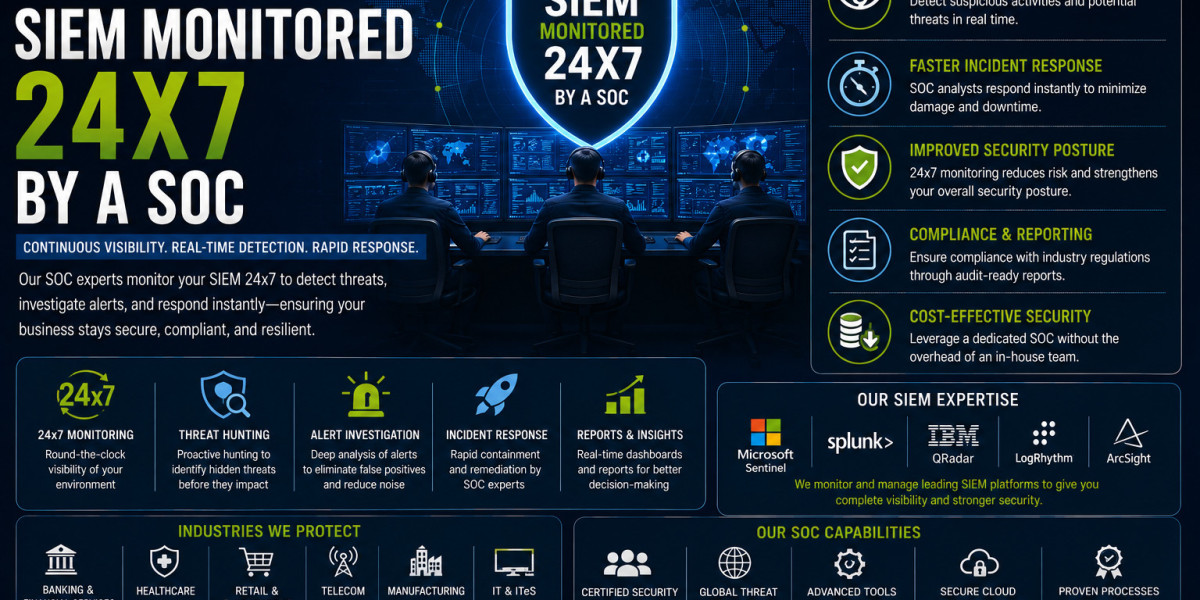
For Indian ICT organizations, SIEM monitored 24x7 by a SOC combines centralized security event analysis with continuous oversight from security operations professionals. Instead of depending only on internal staff to investigate alerts, the model provides ongoing monitoring, investigation, escalation, and incident response across connected networks, endpoints, cloud services, and applications.
In house security or an external SOC
Operating model: ICT organizations often manage complex environments for connectivity, communications, hosting, software, cloud, and technology services. The choice between building internal security operations and working with external soc providers depends on staffing, technology coverage, operational maturity, and the level of continuous monitoring required.
An internal team can provide close knowledge of business systems and existing workflows. An external SOC model can add dedicated security monitoring and analyst capacity without requiring the organization to operate every part of a security operations function itself.
The decision should therefore begin with operational requirements rather than assuming that one model fits every ICT business.
How do soc providers versus in house security teams in India compare?
Soc providers versus in house security teams in India differ mainly in how monitoring responsibilities, staffing, technology management, and incident escalation are organized. An internal model keeps security operations within the organization, while an external model assigns agreed monitoring and response responsibilities to a specialist provider.
Where ICT environments create security pressure
Technology complexity: An ICT organization may have network infrastructure, customer-facing applications, cloud environments, administrative systems, remote access services, and endpoints operating together. Security events can cross these boundaries, making isolated monitoring less useful.
For example, an unusual administrator login may not appear significant by itself. If it is followed by unexpected access to network infrastructure and abnormal endpoint behavior, the combined pattern deserves closer investigation.
A SIEM helps centralize these signals, while SOC analysts can examine their context and determine whether escalation is warranted.
What an in house model requires
Resource commitment: Running internal security operations involves more than purchasing a SIEM platform. Organizations need people who can monitor alerts, investigate incidents, maintain detection rules, document events, coordinate response, and manage the underlying security tooling.
Continuous coverage also requires appropriate staffing arrangements and clear ownership outside normal office hours. For an ICT organization already managing demanding infrastructure operations, adding these responsibilities can create competing priorities.
An internal model can still be appropriate where an organization has established security expertise, defined processes, and sufficient resources to maintain continuous operations.
What an outsourced SOC changes
Shared responsibility: An outsourced SOC changes who performs defined security operations tasks, but it does not remove the organization's responsibility for its environment. The service should establish exactly which activities belong to the SOC and which remain with internal IT, security, network, or application teams.
With SIEM monitored 24x7 by a SOC, security events can be collected continuously and reviewed according to agreed detection and escalation processes. Internal teams can then receive prioritized information rather than having to manually examine every security notification.
The effectiveness of this arrangement depends heavily on integration, communication, and clearly documented response procedures.
Comparing the two approaches
Decision criteria: ICT leaders should compare operating models according to the organization's actual environment rather than focusing only on service descriptions.
Area | In house security team | External SOC model |
Staffing | Internal recruitment and coverage | Specialist external analysts |
SIEM operations | Managed internally | Managed according to service scope |
Alert investigation | Internal responsibility | SOC analysts handle agreed alerts |
After-hours coverage | Requires internal arrangements | Can be included in service scope |
Infrastructure knowledge | Direct internal familiarity | Built through onboarding and integration |
Escalation | Internal workflow | Defined client and SOC workflow |
Scaling | Requires additional internal resources | Can be adjusted with service requirements |
What ICT leaders should examine before outsourcing
Service boundaries: A provider should clearly state what is monitored, what is investigated, what triggers escalation, and what actions require customer approval. Ambiguous responsibilities can slow incident handling when an actual security event occurs.
Integration depth: Ask how the SOC will connect with existing network, endpoint, identity, cloud, and application environments. A monitoring service is more useful when important security telemetry is available and correctly interpreted.
Detection quality: Review how alerts are prioritized and how recurring false positives are handled. ICT teams should understand how detection rules are tuned as the environment changes.
Communication process: Establish named contacts, escalation channels, severity definitions, and incident documentation requirements before operational monitoring begins.
A practical ICT scenario
Operational example: Imagine an Indian communications technology company operating customer portals, internal identity services, network equipment, and cloud workloads. An employee account begins authenticating from an unusual location while related activity appears across a sensitive application.
With SIEM monitoring connected across relevant systems, the event can be correlated rather than reviewed as separate notifications. SOC analysts can investigate the sequence, determine its severity, and escalate it to the appropriate internal team when action is required.
This approach can be useful when the ICT organization wants internal specialists to focus on infrastructure and business operations while security analysts handle continuous event investigation.
India considerations for ICT security
Governance needs: Indian ICT organizations should map their security monitoring arrangements to applicable contractual obligations, privacy requirements, internal policies, and incident-management expectations. Where relevant, organizations should also consider CERT-In directions and the Digital Personal Data Protection framework when designing security processes.
Security monitoring should support governance rather than operate as an isolated technical function. Logging, access control, incident records, and escalation procedures should align with the organization's wider risk-management practices.
What should ICT leaders ask about soc providers versus in house security teams in India?
ICT leaders should compare coverage, staffing, integration, response ownership, escalation procedures, reporting, and operational flexibility. They should also determine which security responsibilities must remain internal and which can be assigned to an external SOC.
Practical steps for making the transition
Map the environment: Identify critical applications, networks, cloud assets, endpoints, identities, and security devices that need visibility.
Define ownership: Document who investigates alerts, who approves containment, and who communicates during an incident.
Prioritize signals: Focus initial monitoring on systems where suspicious activity could create significant operational or customer impact.
Test escalation: Use controlled scenarios to confirm that the SOC and internal teams know how to communicate and respond.
Review continuously: Security monitoring should evolve as infrastructure, applications, users, and business requirements change.
FAQ
Can an ICT company combine an internal security team with an external SOC?
Yes. A hybrid arrangement can assign continuous monitoring and specific investigation tasks to an external SOC while internal specialists retain control over infrastructure, applications, and remediation decisions.
Does an external SOC replace an ICT security team?
Not necessarily. The service can complement internal personnel by handling defined monitoring and investigation responsibilities while internal teams retain ownership of business systems and security decisions.
What makes SIEM monitoring useful for ICT organizations?
SIEM monitoring brings security events from multiple technologies into a centralized analysis process. When supported by SOC analysts, it can help identify relationships between events and provide a structured path for investigation and escalation.
IBN Technologies offers managed SOC and SIEM services for organizations seeking continuous monitoring, threat detection, and structured security operations.
Contact Us
IBN Technologies
Phone: +91 20 6768 0404
Email: sales@ibntech.com